What's going on in security: 8–15 November, in a nutshell
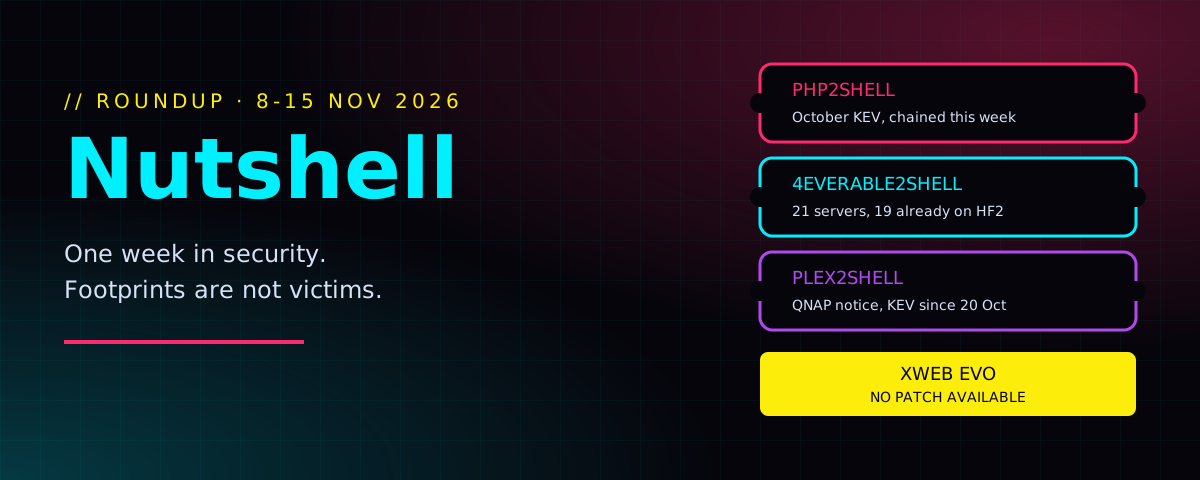
Coffee first. Window: 8–15 November 2026, through 16:20 CET on the 15th. NVD figures below are from 20:18 CET. Last week: SSHole is in KEV now, and Barracuda is no longer just research.
Patch this before your coffee gets cold
Catalog 2026.11.13, released 13 November 21:24 CET, unchanged through 15 November 16:13. Ransomware use: Unknown.
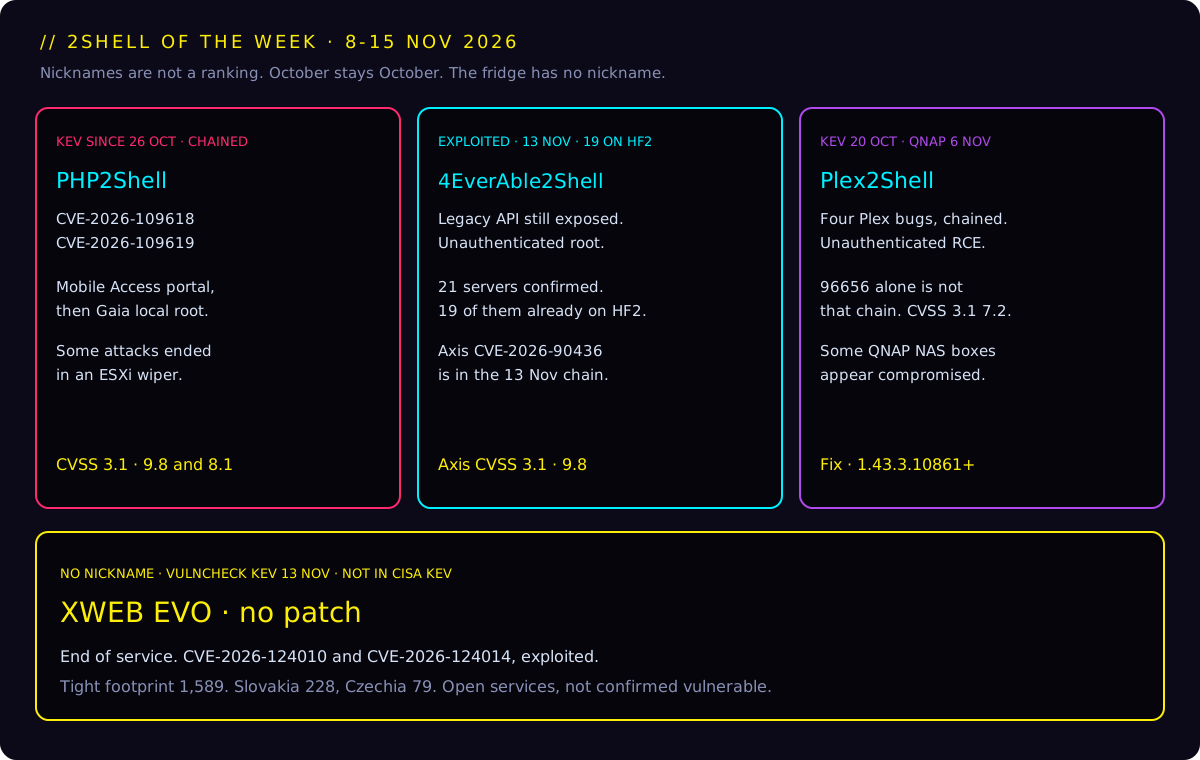
Portal, root, then a wiper
CVE-2026-123039 is local root in Gaia. DynamicCLI does not authorize a world-writable local socket. Published 12 November, KEV 13 November, due 16 November. CVSS 3.1 7.8 CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H, source [email protected]. The way in is PHP2Shell, KEV since 26 October: CVE-2026-109618 CVSS 3.1 9.8 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H and CVE-2026-109619 CVSS 3.1 8.1 CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H, both sourced [email protected], both with a vendor CVSS 4.0 9.2 from [email protected].
Check Point has seen the local bug against “a couple of dozen customers.” The Hacker News, SecurityWeek and BleepingComputer describe unpatched Mobile Access portals, PHP webshells, the PhiliKit backdoor, internal scanning, and some ESXi SSH as vpxuser with the destroy_v6 wiper and DREAM_ANNEXATION.txt. 30 October hit Israel, some of it destructive; 2 November was broader. Attribution is low confidence. Affected: R81, R81.10, R81.20, R82, R82.10 and R82.20 of Force Firewalls, Management and Log Servers, Multi-Domain Security Management and Log Server, and Maestro Orchestrator. Install the fix and patch PHP2Shell. If you cannot today, take Mobile Access off the internet. IOC: 130.94.19[.]204. vuln: was 0. Ignore unscoped PHP totals (~936,120 and ~1,768,032). GreyNoise: 111 source IPs for CVE-2026-109618, and 0 for the other two.
Anyone on the IRC network
CVE-2026-114713: in 6.0.0 before 6.2.7.1 the labeled-response module does not escape the IRCv3 label tag, so on two or more linked servers an ordinary user can inject server-to-server commands with server authority. Hotfix 7 November, attempts from 8 November, KEV 13 November, due 16 November. CVSS 3.1 8.6 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:H/A:N, source [email protected]. The maintainer called it the most critical UnrealIRCd issue in 15 years: “bad guys exploiting this issue on the internet right now.” News, The Hacker News, oss-security. Hot-patch bundle-20261107 (6.0.0–6.2.7, no restart reported) or upgrade to 6.2.7.1. Spamfilter only if you cannot. vuln: was 0 on 14 November; the banner footprint was 74.
HF2 did not finish the job
“4EverAble2Shell” (also Agent2Shell) still gets unauthenticated root on on-prem N-central when the non-default Legacy API is exposed, after HF2 covered CVE-2026-125878 through CVE-2026-125883 and CVE-2026-91000. An appliance ID reaches SYSTEM on a Windows agent. On 13 November: 21 servers, 19 already on HF2, chained with Apache Axis CVE-2026-90436, CVSS 3.1 9.8 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, source 134c704f-9b21-4f2e-91b3-4a467353bcc0. N-central’s own scores were not retrieved. Hosted N-central was described as unaffected by the Legacy API issue. “HF1 or later” is unresolved next to that 19. Victims, PoCs, BleepingComputer. XMRig via jup.sh from 157.20.241[.]16. Disable the Legacy API. A title is not a Legacy-API host.
No patch.
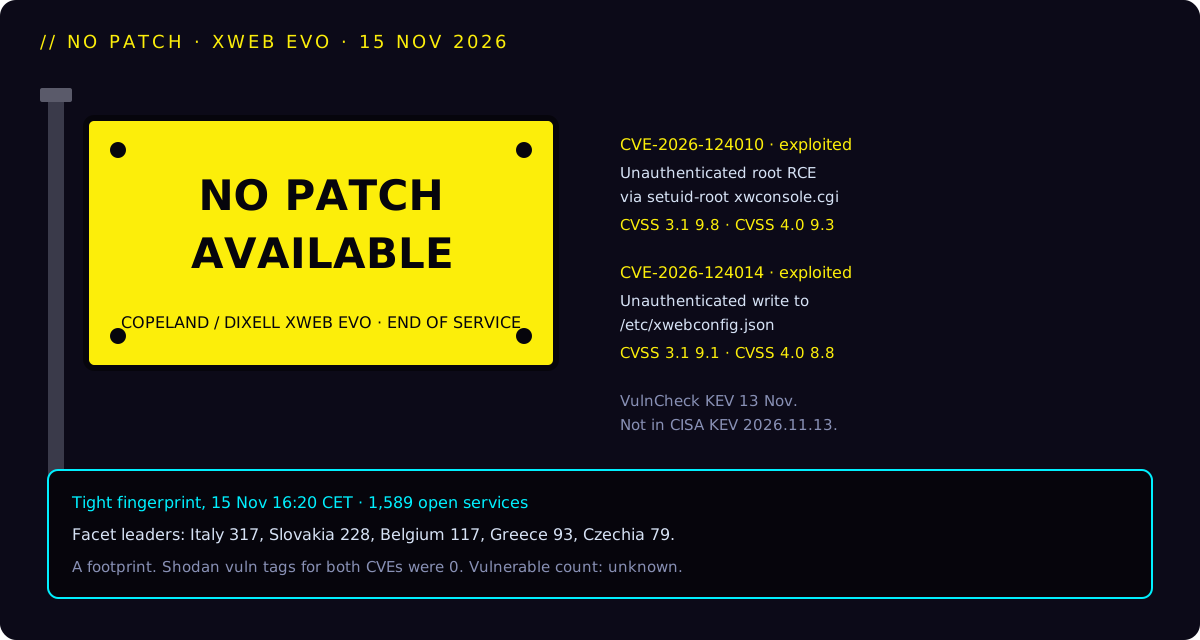
VulnCheck disclosed 14 root-impact bugs in Copeland (Dixell) XWEB EVO. The product is end of service. Two bugs are exploited. CVE-2026-124010, unauthenticated root RCE via setuid-root xwconsole.cgi: CVSS 3.1 9.8 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H and CVSS 4.0 9.3 CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N. CVE-2026-124014, unauthenticated write to /etc/xwebconfig.json via config.lua: CVSS 3.1 9.1 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:H and CVSS 4.0 8.8 CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:H/VA:H/SC:N/SI:N/SA:N. Source on all four: [email protected]. VulnCheck KEV on 13 November. Not in CISA catalog 2026.11.13. Advisory.
Tight fingerprint, 15 November 16:20: 1,589 open services. Slovakia 228, Czechia 79. Italy leads the facet at 317 and is not a column on the chart. vuln: was 0. Ignore http.title:"XWEB" (8,905) and title-only "XWEB EVO" (1,634). Off the internet, VPN only, migrate to XWEB PRO. 228 is a footprint, not 228 owned compressors.
SCKit and Plex2Shell
CVE-2026-84869 has been in KEV since 11 September. Guest-to-host, CVSS 3.1 9.9 CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H, source 7d616e1a-3288-43b1-a0dd-0a65d3e70a49. SCKit uses it and RelayTrap to hijack technician sessions and .ASPXAUTH. The Hacker News, BleepingComputer, ConnectWise. Huntress, the same day: rogue clients on 288 endpoints in 48 organizations, including RMM+ 1.0.31/1.0.32 with a blank key. Related stories, not one CVE. C2 ns.mo7sen[.]dev. IoCs 185.99.255[.]28 and 155.94.150[.]39. GreyNoise returned HTTP 429.
Four Plex bugs, chained, are unauthenticated RCE as the Plex process. CVE-2026-96656 alone is an authenticated file write: CVSS 3.1 7.2 CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H and CVSS 4.0 8.6 CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N, source 9119a7d8-5eab-497f-8521-727c672e3725. Not the chain. KEV since 20 October. QNAP, via SecurityWeek: Plex on some NAS devices appears compromised. The bugs are in Plex, not QTS or QuTS hero. Update to 1.43.3.10861 or later. A patch does not remove a payload.
SSHole, CVE-2026-123158, is now KEV (9 November, due 12 November). CVSS 3.1 8.1 CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H, source [email protected]. Fix unchanged: 10.6p2. The tag panel is not a musl census. Barracuda CVE-2026-116606 (CVSS 3.1 9.8 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, source [email protected]; Mandiant CVSS 4.0 9.3) restores a crafted backup to admin. CVE-2026-111560 (CVSS 3.1 7.2 CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H, same NVD source; Mandiant CVSS 4.0 8.6) chains that to root. A small number of organizations were hit. KEV 10 November, due 13 November. Upgrade ESG to 9.4.0.030. 9 November also added GPUStack CVE-2026-102895 (CVSS 3.1 9.8 CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, source [email protected]; SANS saw 144.91.73[.]103; fix 2.2.0 and strip X-Gpustack-Real-IP), plus FreeSWITCH CVE-2026-116779 and Aspera Faspex CVE-2026-123218. 10 November includes Chrome CVE-2026-125350, the 8th Chrome 0-day of 2026, among others.
Worth knowing
Aikido and BleepingComputer: 4,837 hijacked GitHub accounts, wfx-loot in 1,806+ repos, later 61,764 repos probed and secrets taken from at least 1,835, including cloud OIDC. SafeDep: 8,093 repos with malicious commits. Hunt “docs: dependency audit notes”, wfx-docs, wfx-loot, WFX-BEGIN, Azure FIC wfx-ci-, digitalelvis/neuronai-studio 3.14.3 and onuragtas/docker-env v1.0.278/.280. Accounts and repos, not hosts.
A stolen Fireworks AI key copied Cursor traces for users without Privacy Mode. Credentials in some of them published malicious Claude Code 2.1.312 and 2.1.313 for about 11 hours. Update: 14 November, 18:27 CET. BleepingComputer, The Hacker News. “At most 5,000” is an exposure estimate. Coding errors likely broke that backdoor where SSH was already off. Anthropic’s extension, Open VSX and Privacy Mode content were not affected, per Cursor.
Quantum Systems detected “hostile actors” in late October. Der Spiegel and the Financial Times, cited on 13 November, described a malicious QBase update from a compromised vendor server. QBase plans the Vector drone, Falke in German service. Additional reporting said the German armed forces grounded the systems as a precaution. No named actor, no CVE, no install count. Verify any surprise update.
Citrix patched 12 NetScaler flaws on 12 November. No known exploits in this pack. CVE-2026-120868 and CVE-2026-120869 are CVSS 4.0 9.3, source in NVD 50a63c94-1ea7-4568-8c11-eb79e7c5a2b5. CTX697305, CTX697320.
Meanwhile in the underground
Weekday public digests, 9–13 November, last check around 08:55 CET on the 13th. No weekend pass. Seller ads are not breaches. I am not linking markets.
KrebsOnSecurity reportedly tied Qilin’s admin “Haise” to a person, using RAMP direct messages indexed by Intel 471 and old Exploit and XSS handles. An allegation. No charges filed. He cites NCC Group for at least 365 claimed victims in three months. The identity is unproven.
Operation TorNado: Europol reported 354 arrests on 12 November. No tracked forum was named.
Two charts, two claims
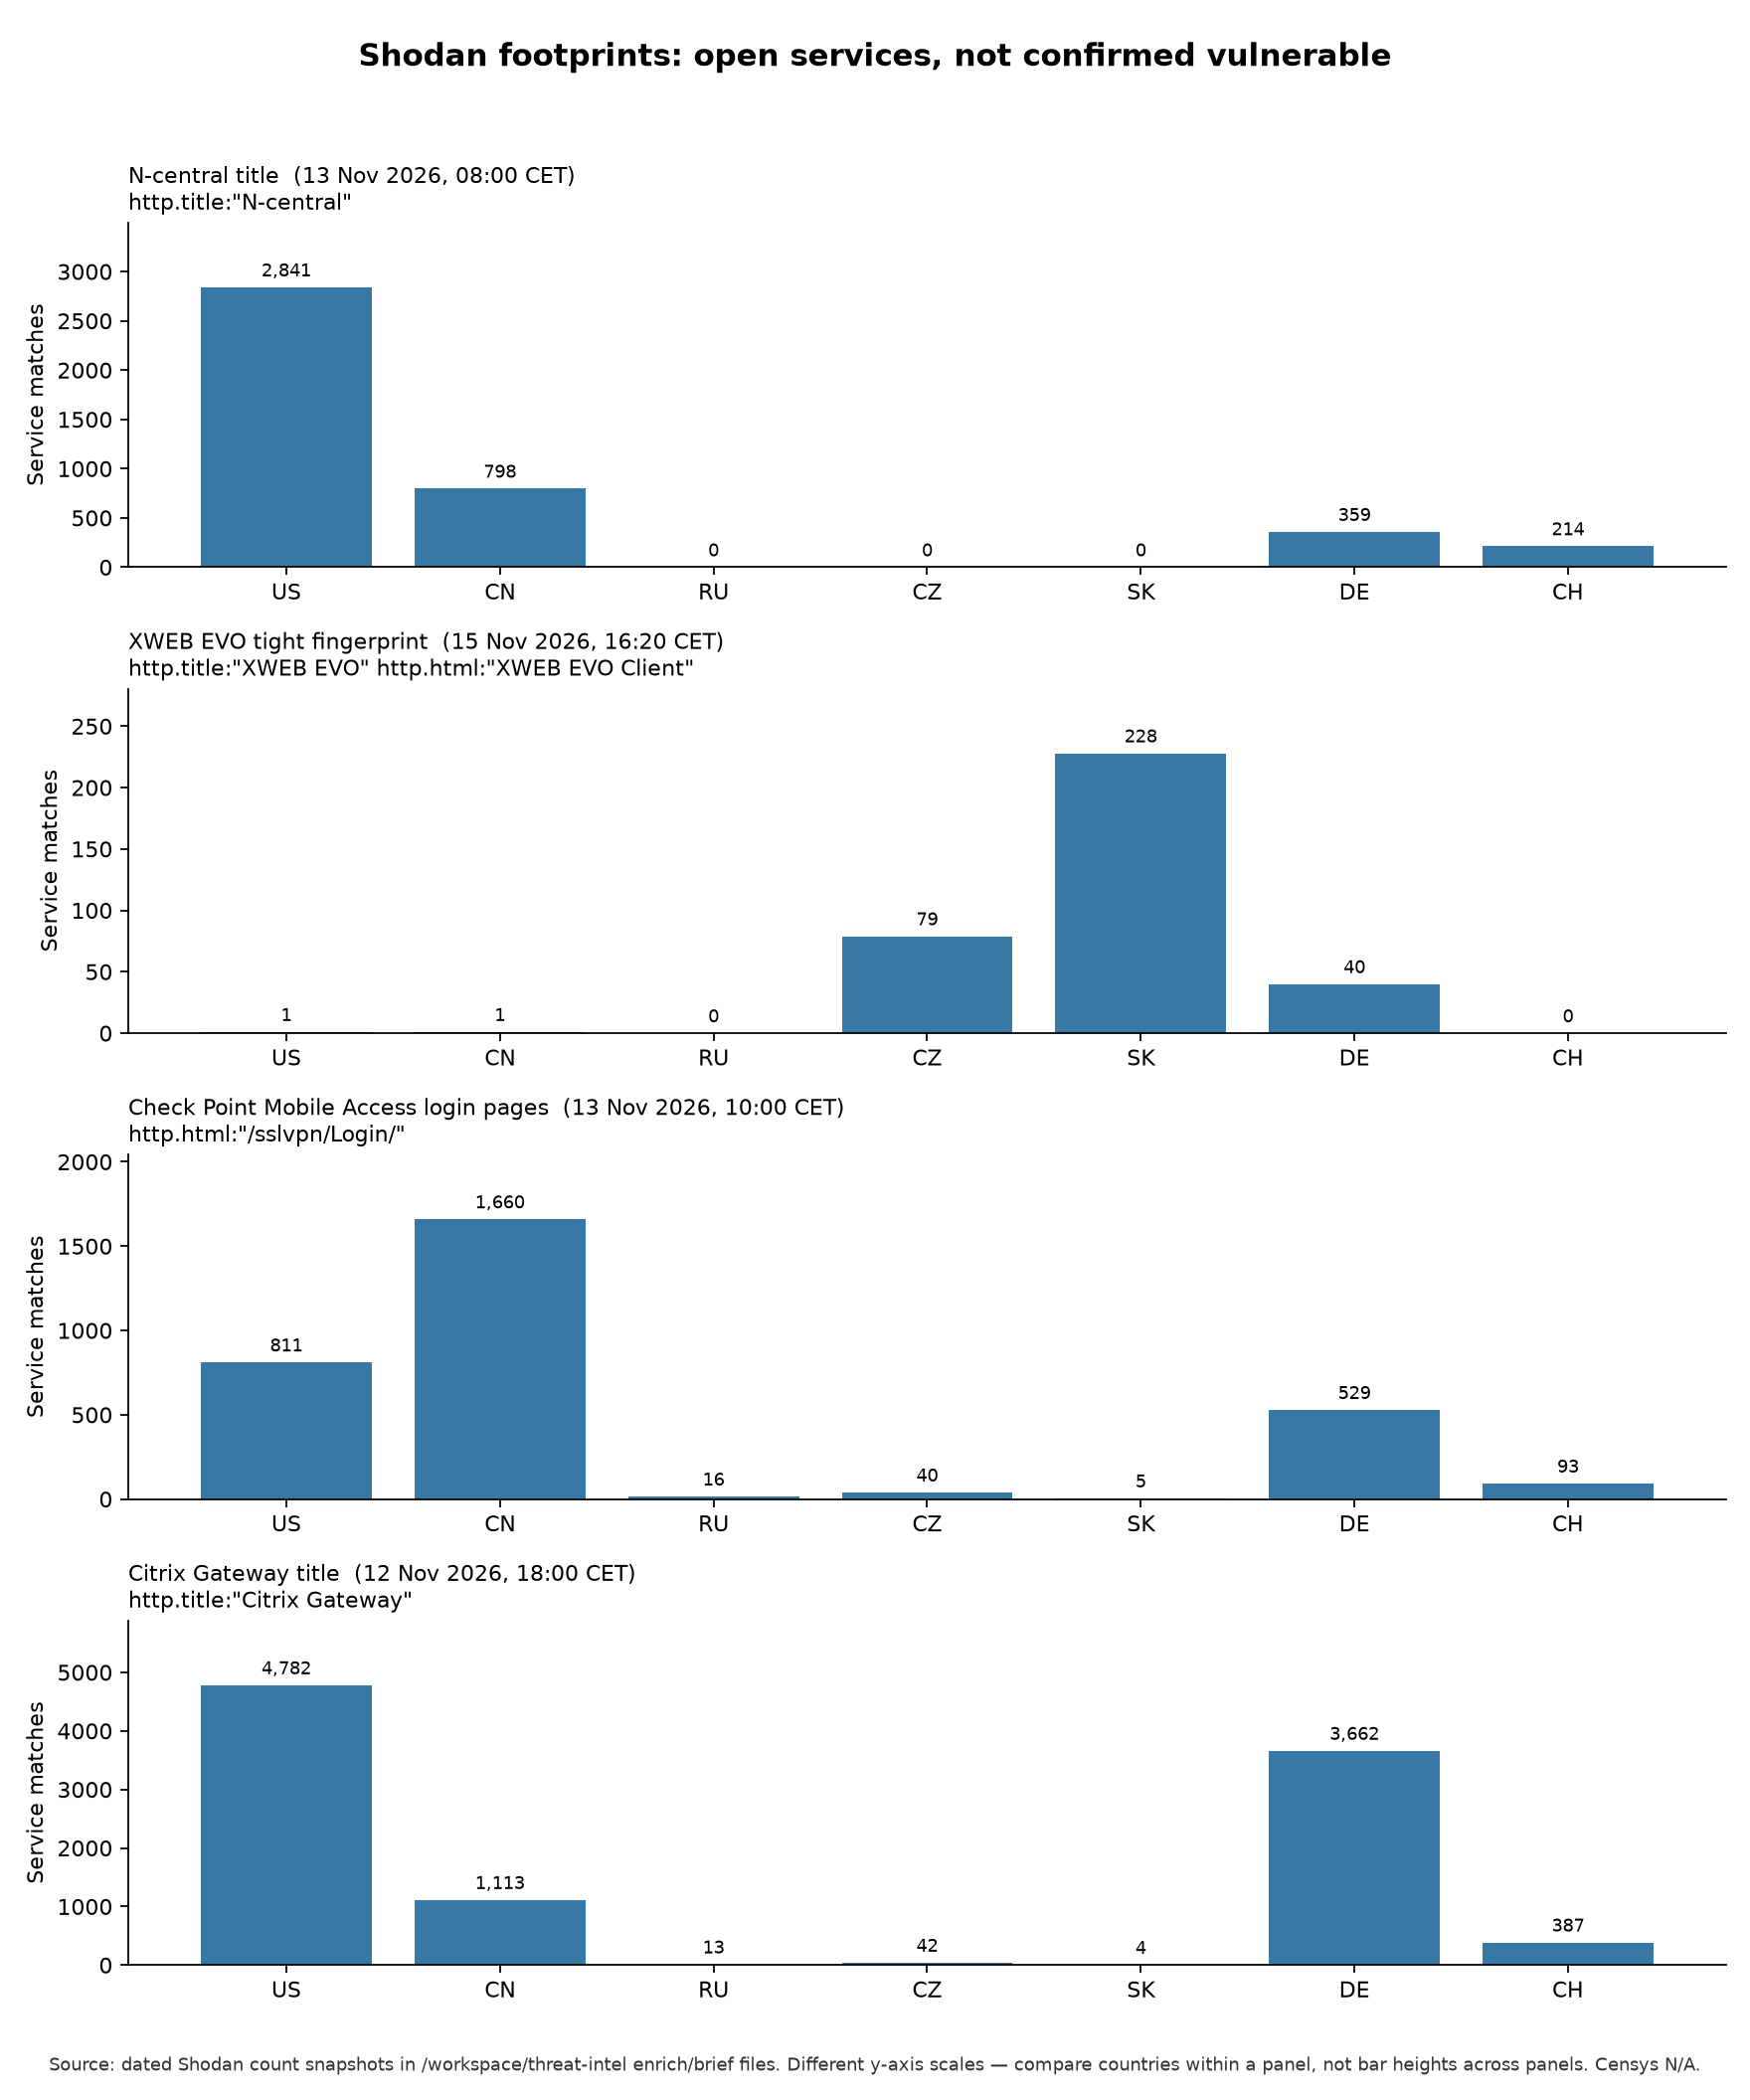
Compare countries inside a panel. The y-axes do not match, and the seven countries do not sum to the global. N-central 11,923, XWEB 1,589, Check Point login pages 6,565, Citrix Gateway 21,957.
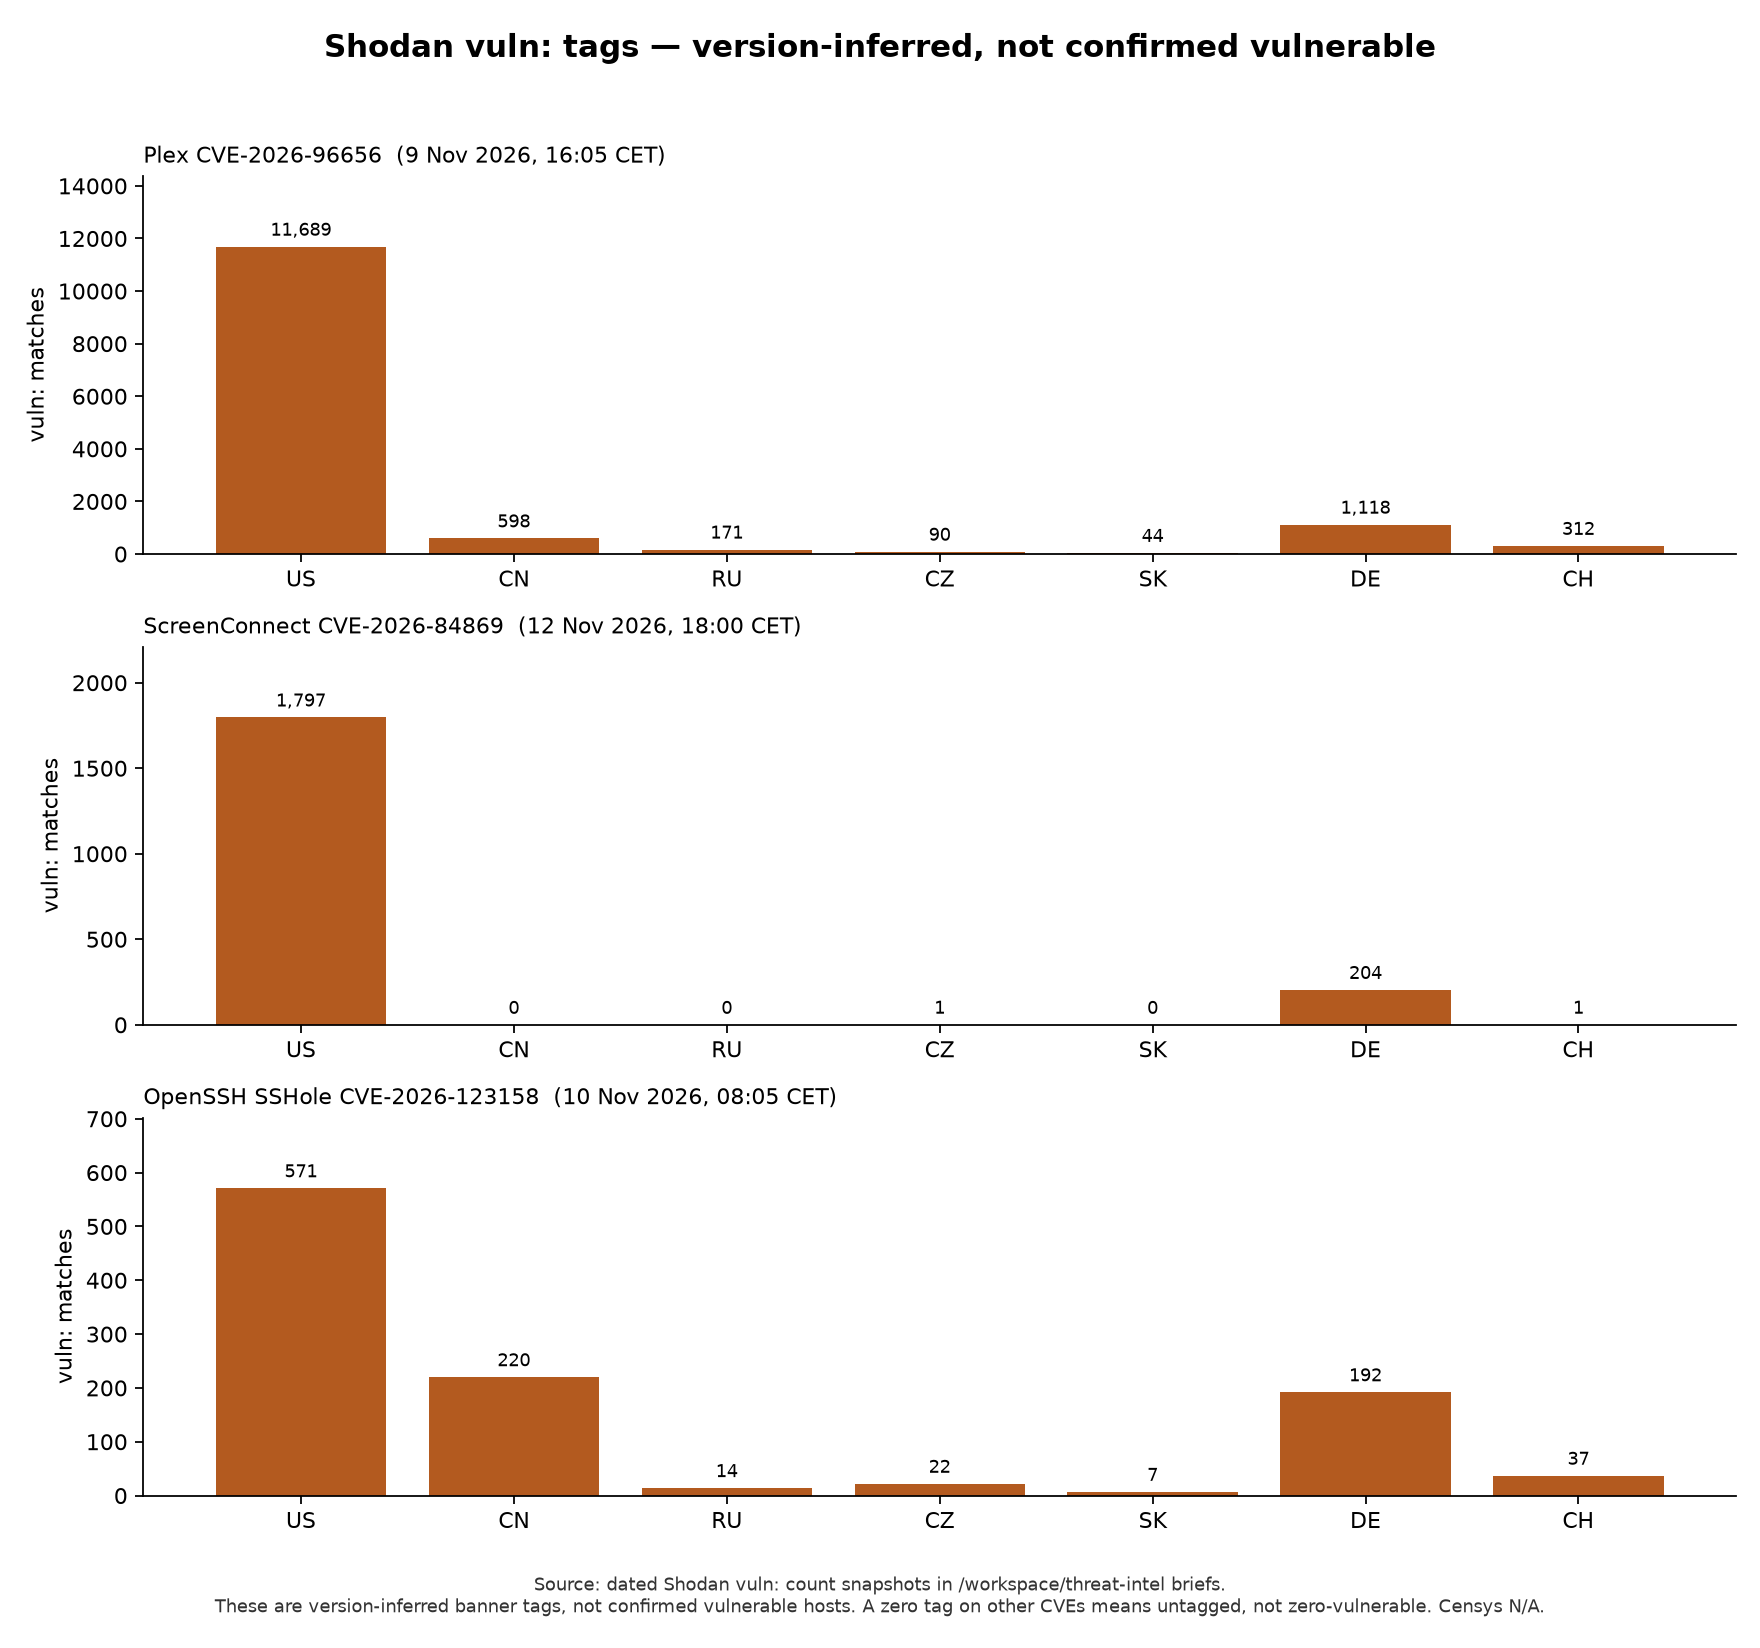
Shodan builds vuln: tags from version banners. Plex CVE-2026-96656 36,084. ScreenConnect CVE-2026-84869 9,387. SSHole 2,174. A zero tag means untagged: Check Point’s Gaia bug, UnrealIRCd, both XWEB IDs, the Axis bug, both Barracuda IDs.
vuln: tag is inferred from a version banner. Censys returned HTTP 403, so there are no Censys counts. GreyNoise returned no data or was rate-limited on several items. A GreyNoise number counts source IPs, with no time filter, and a zero does not clear a CVE.Then finish the cup
Patch the KEV rows, then unplug XWEB. Slovakia got a footprint and no patch.